Early access · invite-only
Cut your cloud costs. Stop paying for resources you don’t use.
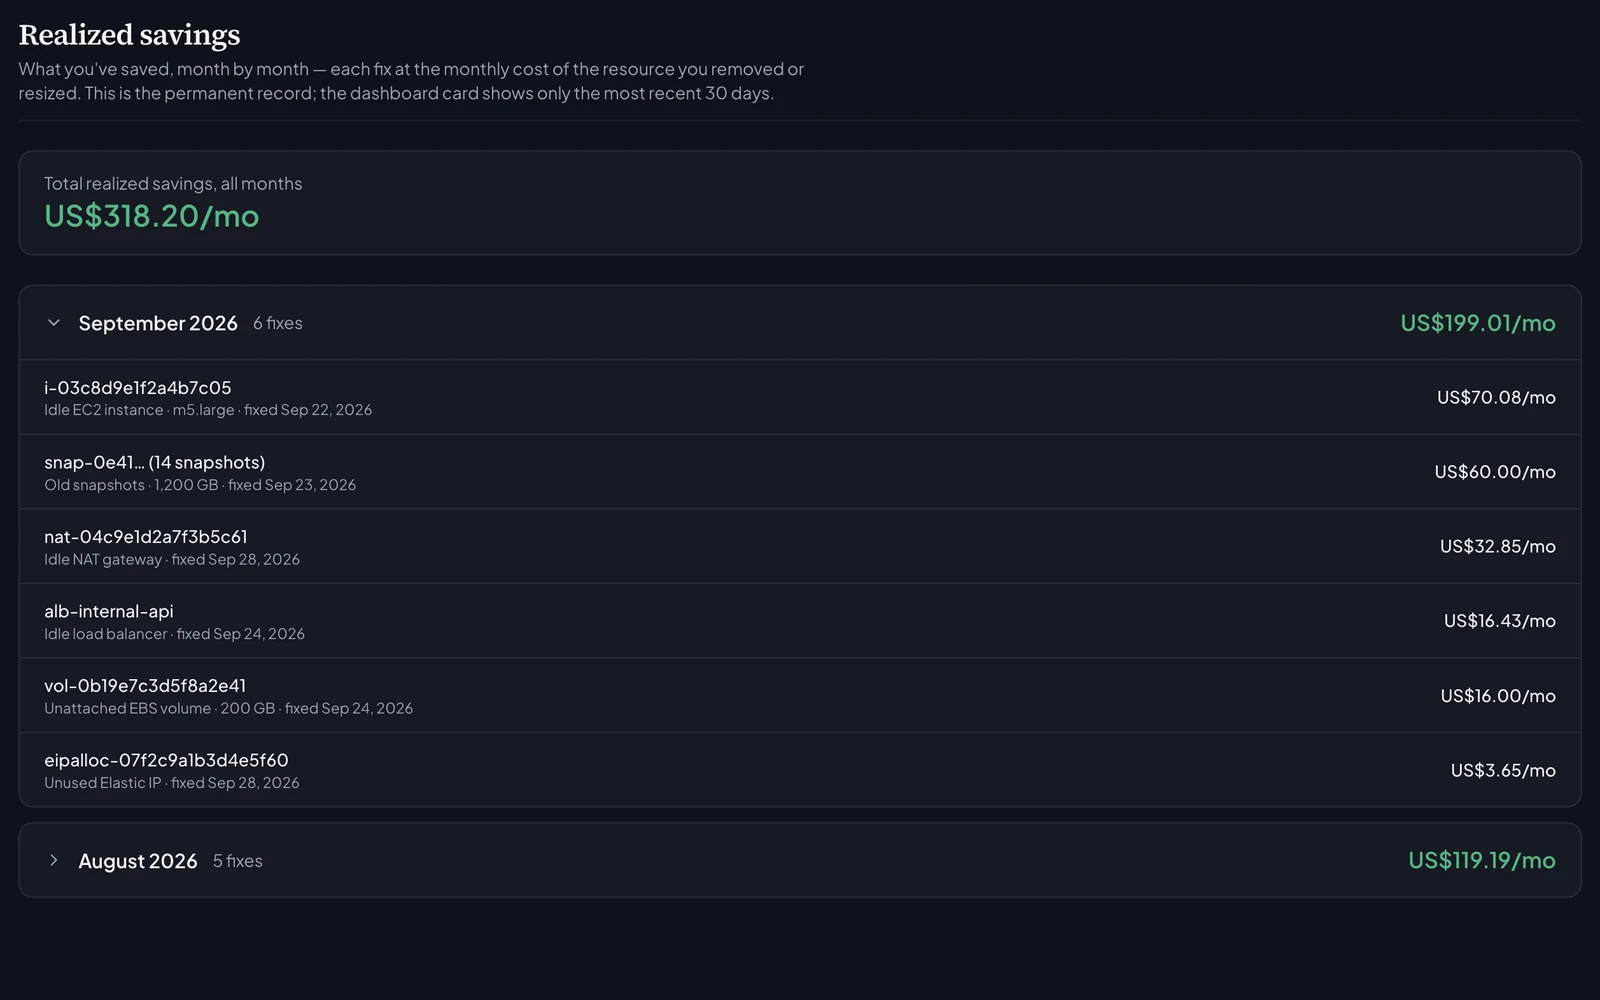
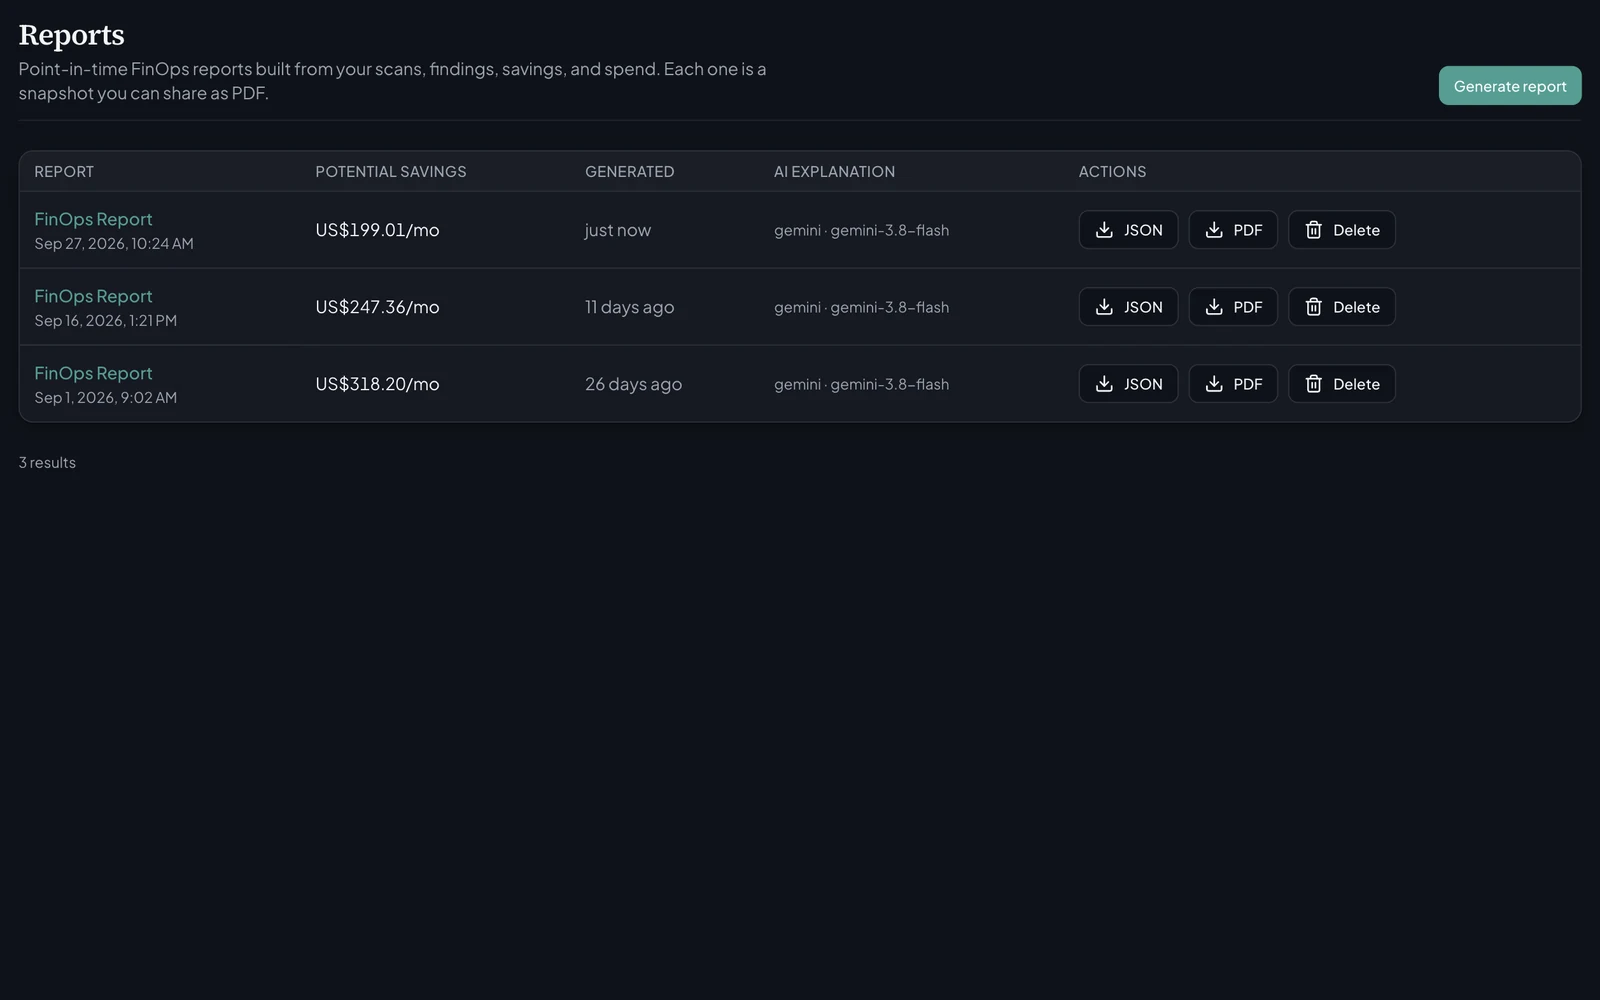
VeriKost is a cloud cost optimization tool. It scans your cloud account, finds idle and oversized resources, and shows exactly how much each fix cuts from your cloud bill.
Supported clouds
- AWSLIVE
- Google CloudLIVE
- AzureSOON
- OCISOON
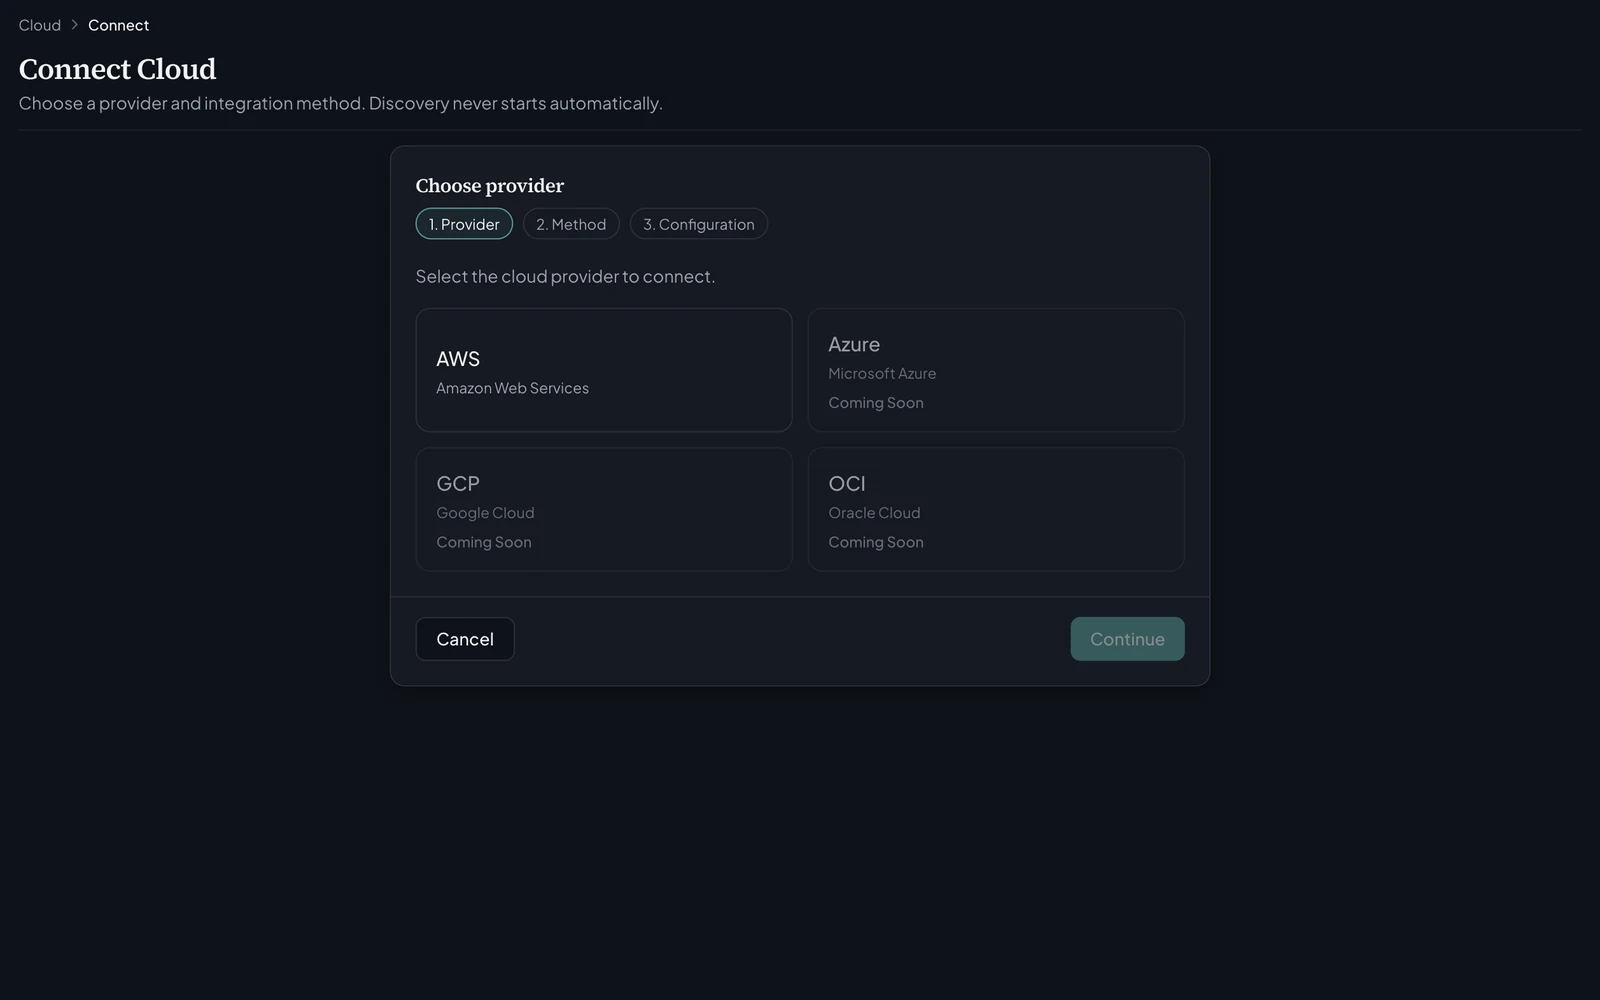
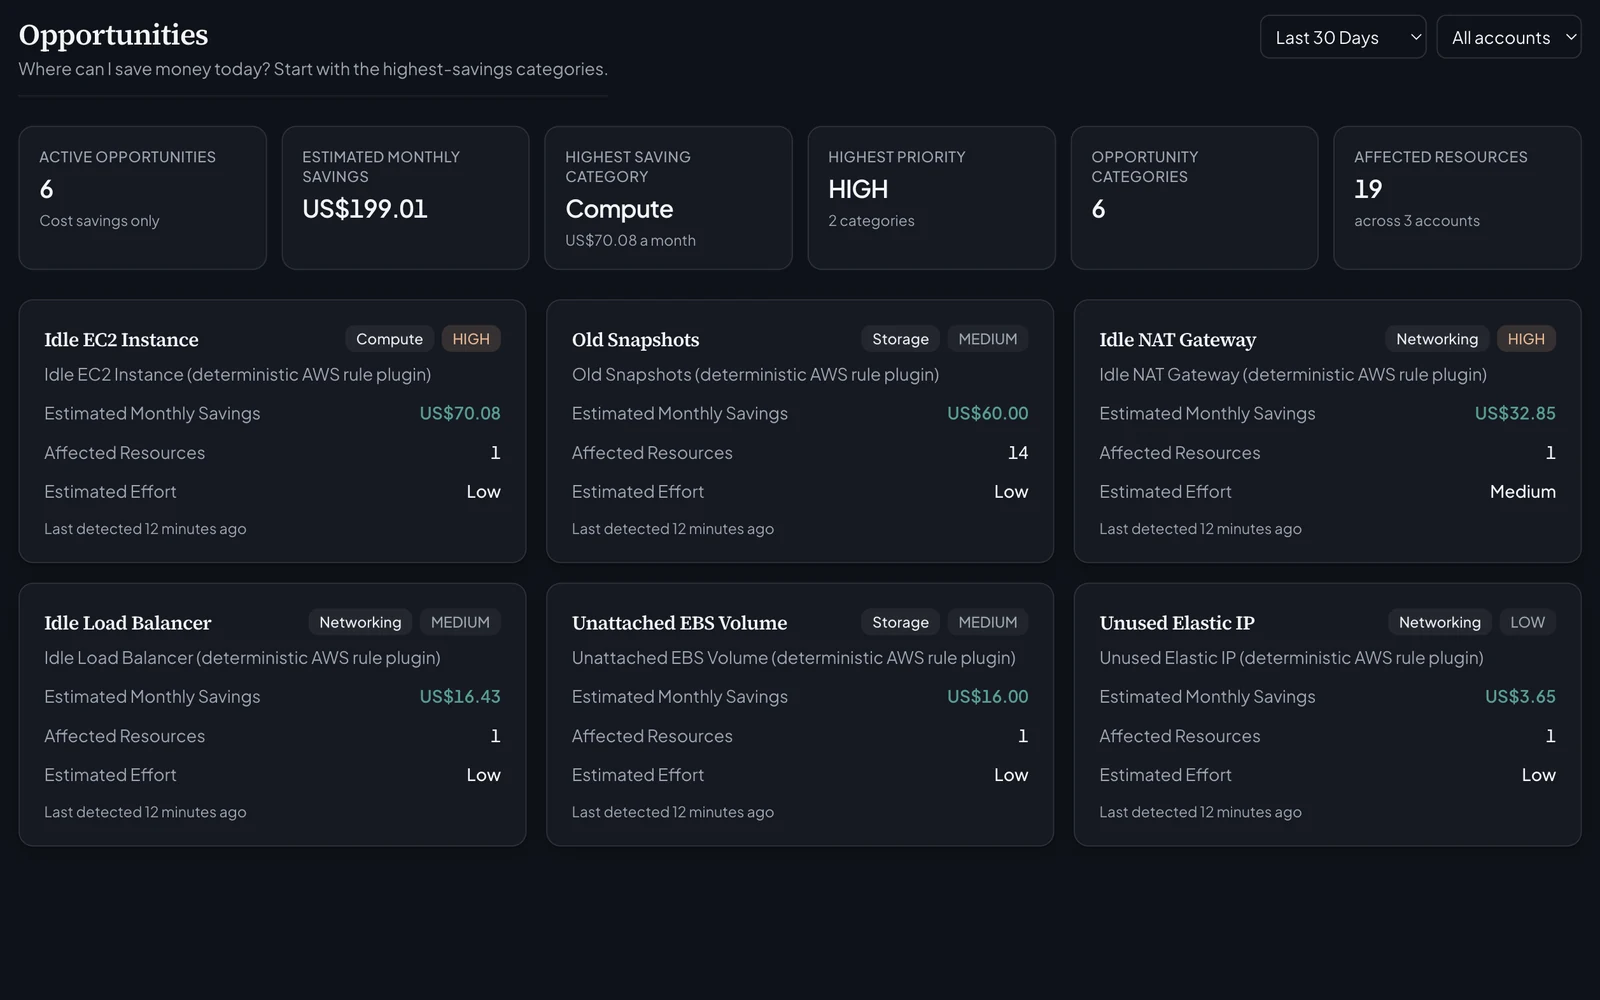
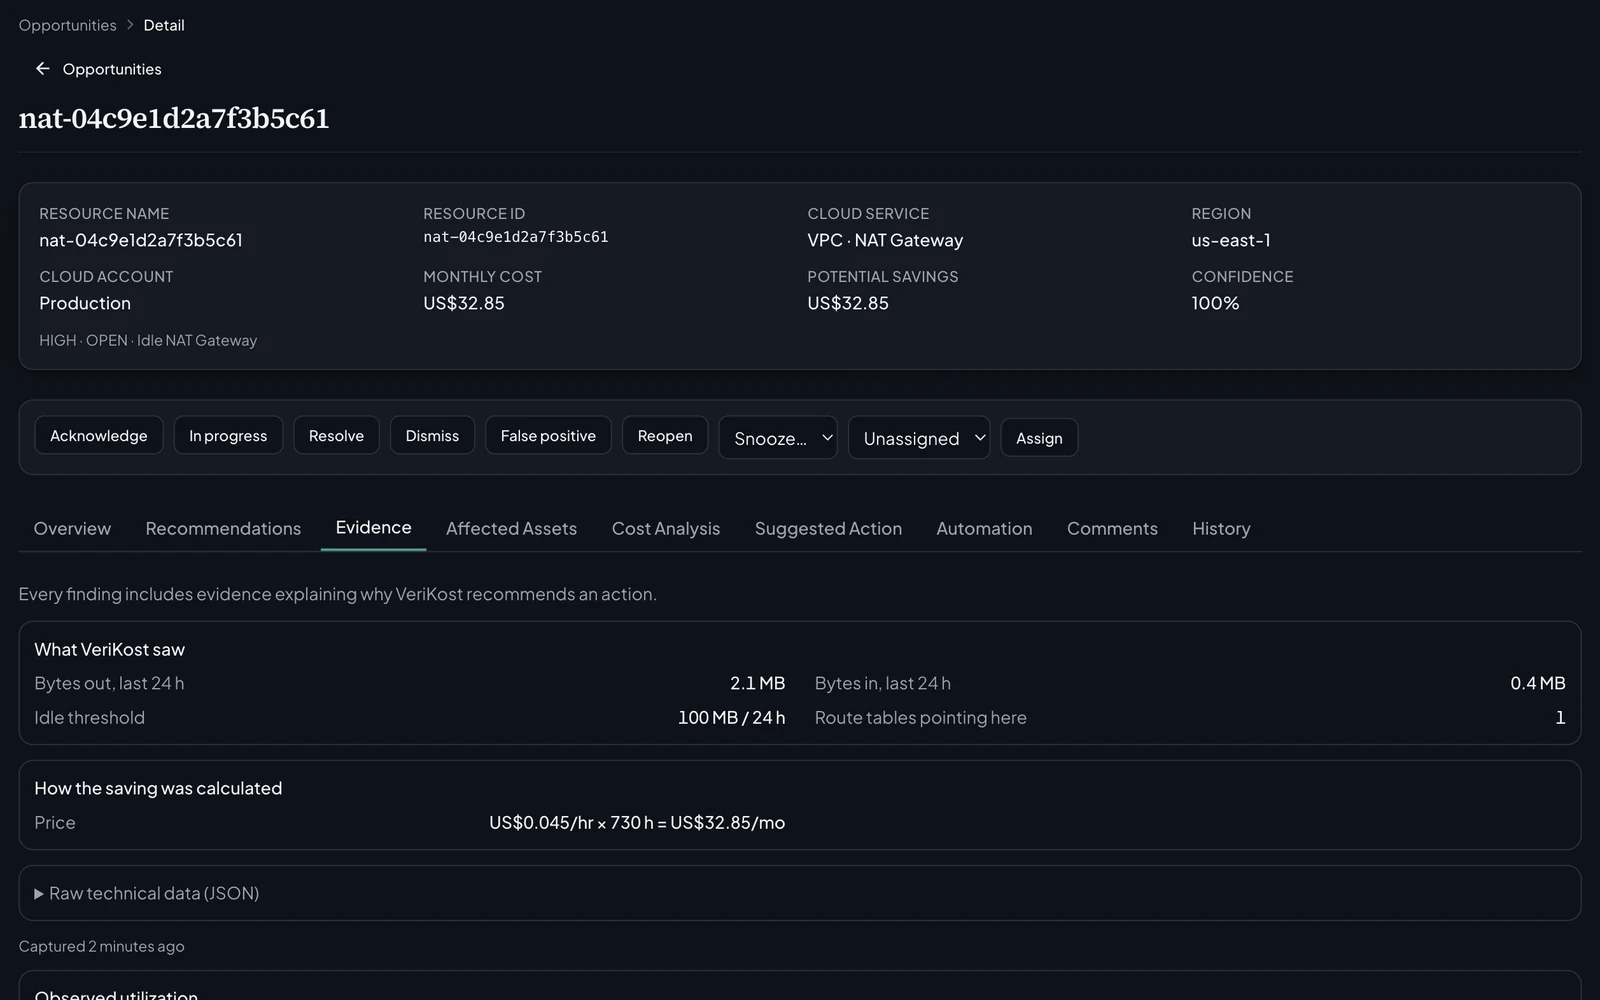
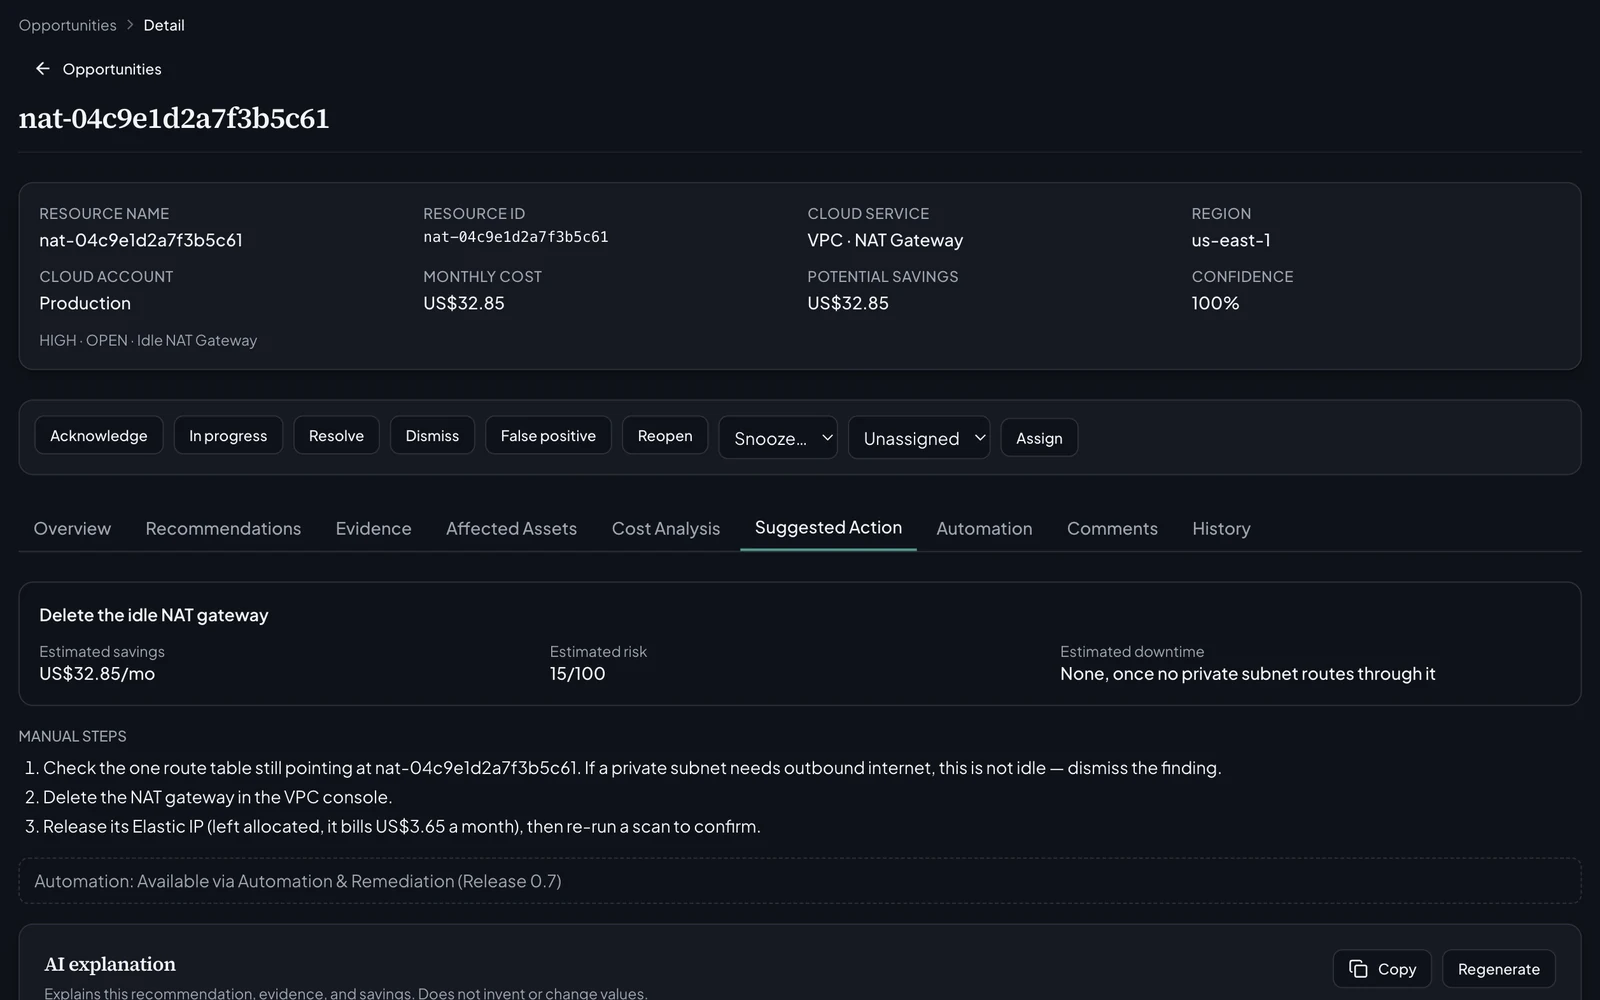
You connect with a read-only role.
We give you the policy. You create the role in your own AWS console and paste its ARN. There is no password and no access key to hand over.
- Describe, list and get. Nothing that writes.
- Discovery never starts on its own — you press the button.
- Delete the role and we're out.
64 checks on AWS and 34 on Google Cloud, across the services that quietly cost the most.
AWS · 64 checks
Compute
- EC2
- EKS
- Fargate
- Lambda
- SageMaker
- WorkSpaces
Storage
- EBS volumes and types
- Snapshots
- AMI snapshots
- EFS
- S3
- CloudWatch Logs
Network
- NAT Gateway
- Load Balancers
- Elastic IP
- Data transfer
Data
- RDS & Aurora
- DynamoDB
- ElastiCache & MemoryDB
- OpenSearch & Redshift
- MSK & EMR
- DMS & MWAA
Commitments
- Savings Plans
- Reserved Instances
Google Cloud · 34 checks
Compute
- Compute Engine VMs
- GKE
- Cloud Run
- Cloud Functions
- Dataproc
Storage
- Persistent disks and types
- Snapshots
- Filestore
- Cloud Storage
- Cloud Logging
Network
- Cloud NAT
- Load balancers
- Static IP addresses
- Data transfer
Data
- Cloud SQL
- Memorystore for Redis
- BigQuery
- Spanner
- Bigtable
Commitments
- Committed use discounts
We can look. We can't touch.
Read-only access
Describe, list and get only, on AWS and on Google Cloud. Nothing that can create, change or delete. Both permission lists are published.
No keys to hand over
On AWS we assume a role you own, with an external ID. On Google Cloud you grant our service account a read-only role; no key is ever created. Remove either and our access ends.
Rules in the open
Every threshold is published. Think one is wrong? Tell us and we'll argue it out.
The complete permission lists for AWS and Google Cloud — every action, no summary — are on the security page.
What’s in your bill?
We’re letting teams in a few at a time. Leave a work email and we’ll send an invite when there’s room.
Invite-only. AWS and Google Cloud.